A lost badge is not always just a replacement-cost issue. For a business, it can raise a larger question: can access cards be cloned? In some cases, yes. Certain older proximity cards can be copied by someone with the right equipment and physical access to the credential. Others use stronger encryption and are far more difficult to duplicate. The difference matters because a copied card can look and operate like an authorized credential while leaving little obvious sign at the door.
For facility managers, business owners, and IT leaders, the practical concern is not whether every card can be cloned. It is whether the credentials protecting your building, staff, equipment, and records are appropriate for the risk your organization manages.
Can Access Cards Be Cloned?
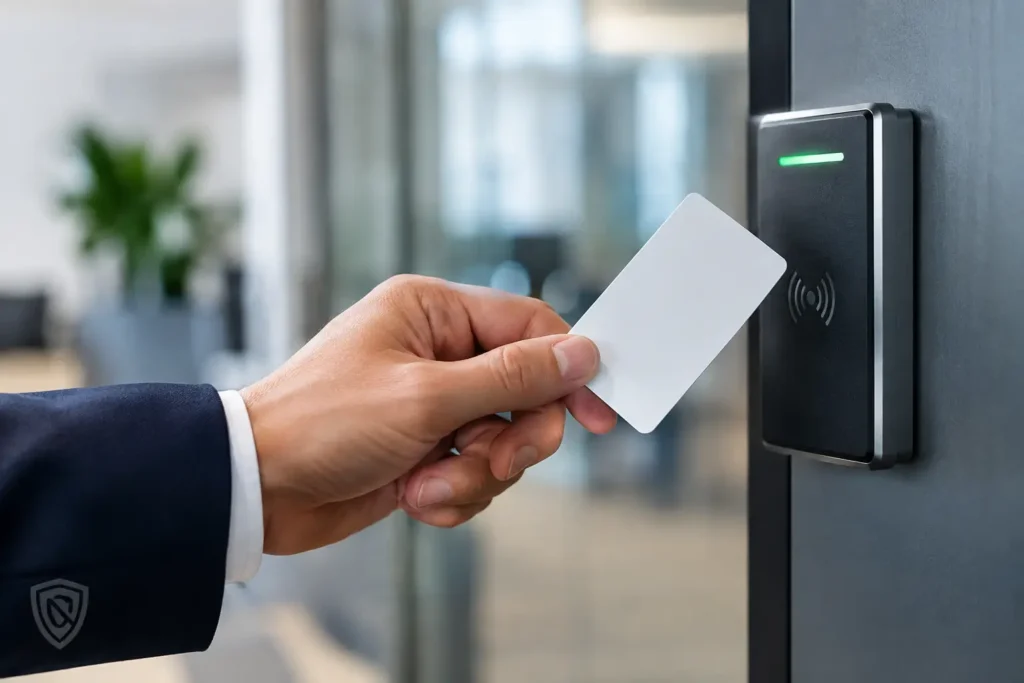
Access cards use different technologies, and their resistance to copying varies widely. Many commercial systems use radio frequency identification, commonly called RFID, or proximity technology. When a credential is held near a reader, it sends identifying information that the access control system uses to grant or deny entry.
Older low-frequency proximity cards often rely on a fixed identifier. If that identifier can be captured, a duplicate credential may be created that presents the same information to a compatible reader. The card itself does not have to be visibly damaged or taken away for long. That is why card cloning is a genuine concern for businesses still using legacy credentials.
Modern encrypted smart cards provide a stronger level of protection. Rather than relying only on a static card number, they can use encrypted communication and authentication methods designed to make copied data unusable. Mobile credentials, which place an approved credential on a managed smartphone, can also add meaningful safeguards when configured correctly.
No credential technology is completely risk-free. However, the right combination of secure cards, properly configured readers, user policies, and system monitoring greatly reduces the opportunity for unauthorized entry.
Why Cloned Credentials Are a Business Risk
A copied access card may allow someone to enter a building after hours, access a restricted room, or move through an employee-only area without forcing a door. That can create exposure well beyond physical theft.
For example, an unauthorized person entering a server room may affect network operations. Entry into a records area could expose confidential client or employee information. In a warehouse, healthcare office, school, or multi-tenant property, unauthorized access can introduce safety and liability concerns as well.
The challenge is that a cloned card can be difficult to identify from normal access reports. The system sees a recognized credential number. If a legitimate employee uses their card in the morning and a copied version is used later that evening, the activity may initially appear to be associated with the same person.
This is where an integrated security approach becomes valuable. Access events, video surveillance, intrusion alarm activity, visitor procedures, and door status monitoring can provide the context that a card report alone cannot. A badge used at an unusual time or location becomes more meaningful when it can be reviewed alongside camera footage and other security activity.
Which Access Cards Face the Greatest Exposure?
The highest concern is generally associated with older card formats that transmit a fixed, unencrypted identifier. These systems were widely adopted because they were dependable, simple to deploy, and convenient for users. Many continue to operate reliably from a day-to-day perspective, but reliability is not the same as credential security.
A business may have greater exposure if it uses older proximity cards, has no requirement for a PIN at sensitive doors, does not regularly deactivate lost credentials, or has limited visibility into access activity. Organizations with high employee turnover, several locations, valuable inventory, sensitive data, or after-hours operations should evaluate their systems especially carefully.
That does not mean every organization needs to replace its entire access control system immediately. A small office with low-risk areas has different needs than a medical practice, financial office, manufacturing facility, or property with multiple tenants. The right path depends on the doors being protected, the value of the assets behind them, and the consequences of unauthorized entry.
How to Reduce the Risk of Access Card Cloning
Credential security begins with knowing what is installed. A professional assessment can identify the card format, reader capabilities, controller age, software status, and whether the system supports more secure credential options. This is often the most useful first step because businesses cannot manage a vulnerability they have not identified.
Upgrade credentials where the risk is highest
A full system replacement may not be necessary in every case. Many organizations start by improving security at the doors that matter most, such as server rooms, cash-handling areas, executive offices, medication storage, telecom closets, or entrances used after hours.
Encrypted smart-card credentials and compatible readers are often the preferred long-term option for organizations replacing legacy proximity technology. Where appropriate, mobile credentials can reduce the need to issue and recover physical cards while giving administrators more control over activation and deactivation.
Add a second verification factor for sensitive areas
For high-security openings, a card alone may not be enough. Requiring a PIN in addition to a credential adds another layer of protection. A copied card without the correct PIN should not grant entry.
This approach has trade-offs. It can slow traffic at busy doors, and users must be trained not to share PINs or write them down near the entry point. Still, for restricted spaces, the added protection can be well worth the minor inconvenience.
Manage credentials as part of employee operations
Access control works best when it is connected to real workplace processes. Issue credentials to named individuals, use appropriate access schedules, and remove access promptly when someone changes roles or leaves the organization. Avoid shared cards whenever possible. A shared credential may seem convenient, but it reduces accountability and makes investigations more difficult.
Lost cards should be reported and disabled immediately, not at the end of the week. A clear policy helps employees understand that a missing badge is a security event, even if they believe it was misplaced off-site.
Review activity and maintain the system
Access reports can reveal patterns that deserve attention, including repeated denied entries, after-hours activity, doors held open, or credentials used at locations that do not fit an employee’s responsibilities. Review does not need to become a daily burden. The goal is to establish sensible reporting and alerts for events that could affect operations or safety.
System maintenance also matters. Firmware, access control software, door hardware, batteries, and network connections all play a role in dependable operation. A strong credential is less helpful if a door is propped open, a reader is offline, or a former employee’s access remains active.
When Should a Business Upgrade Its Access Control System?
Consider an upgrade when existing cards use older technology, when your business has expanded into multiple sites, or when access administration has become difficult to manage. An upgrade may also make sense after a break-in, a lost-card incident, a compliance review, or a change in the type of assets stored on-site.
The best projects balance security with daily usability. Employees need to enter the spaces required for their work without unnecessary delays. Administrators need simple tools to add users, adjust permissions, and review events. Leadership needs confidence that the system supports business continuity rather than creating another operational problem.
For Central Alabama businesses, Comtex can help evaluate existing access control infrastructure, identify practical improvement options, and design a system that works alongside video surveillance, alarms, communications, and network infrastructure. A connected approach helps reduce vendor complexity while giving your team clearer control of the facilities it manages.
A card reader at the door is only one part of protecting a business. The stronger question is whether every credential, door, policy, and supporting system works together to verify the right person at the right place at the right time.